Manage Event Storage
Enable event archives deliberately, expose them in the dashboard, and understand the resulting storage and retention impact.
Decide whether archives are required
Alerts contain events that matched rules; archives can retain events regardless of whether a rule fired. Enable archives only when the investigation, detection-engineering, or compliance value justifies the additional indexer and filesystem consumption.
Before changing configuration, document the expected daily volume, retention period, available storage, and owner responsible for monitoring growth.
Capture a baseline before enabling archives:
sudo du -sh /var/ossec/logs/archives
sudo du -sh /var/lib/wazuh-indexer
df -h /var/ossec /var/lib/wazuh-indexer
Repeat these checks after a representative collection window. Estimate retained
storage as observed daily growth × retention days, add operational headroom,
and define the warning threshold and owner. If growth is not sustainable,
disable archive indexing or reduce retention before continuing.
Detailed event-storage procedure
The original explanation, configuration blocks, service commands, dashboard workflow, screenshots, and retention warning are retained below.
Understand log compression and rotation
Wazuh rotates and compresses older logs while continuing to write new events. Plan retention and monitor free space before enabling full event archives.
Compressed logs and checksum records are stored under /var/ossec/logs/.
Checksums help detect changes when compared with a trusted record; hashing alone
does not authenticate who created a log. See the
Wazuh event-logging guide.
Archive event logs
When archiving is enabled, Wazuh retains received events even when they do not
generate an alert. The configured format determines whether they appear in
archives.log, archives.json, or both under /var/ossec/logs/archives/.
By default, the Wazuh archives are disabled because it stores logs indefinitely on the Wazuh server. When enabled, the Wazuh manager creates archived files to store and retain security data for compliance and forensic purposes.
Note: The Wazuh archives retain logs collected from all monitored endpoints, therefore consuming significant storage resources on the Wazuh server over time. So, it is important to consider the impact on disk space and performance before enabling them.
Enable archiving
Edit the Wazuh manager configuration file /var/ossec/etc/ossec.conf and set the value of the highlighted fields below to yes:
<ossec_config>
  <global>
    <jsonout_output>yes</jsonout_output>
    <alerts_log>yes</alerts_log>
    <logall>yes</logall>
    <logall_json>yes</logall_json>
  </global>
</ossec_config>
<logall> enables or disables archiving of all log messages. When enabled, the Wazuh server stores the logs in a syslog format. The allowed values are yes and no.<logall_json> enables or disables logging of events. When enabled, the Wazuh server stores the events in a JSON format. The allowed values are yes and no.
Depending on the format you desire, you can set one or both values of the highlighted fields to yes. However, only the <logall_json>yes</logall_json> option allows you to create an index that can be used to visualize the events on the Wazuh dashboard.
Restart the Wazuh manager to apply the configuration changes:
Depending on the selected format, Wazuh writes archives.log, archives.json,
or both under /var/ossec/logs/archives/. Rotation and compression reduce the
size of older logs; they do not set a retention limit or guarantee that disk
space will remain available. Monitor storage and define a retention policy.
Visualise events on the dashboard
Edit the Filebeat configuration file /etc/filebeat/filebeat.yml and change the value of archives: enabled from false to true:
Restart Filebeat to apply the configuration changes:
Configure the Wazuh dashboard
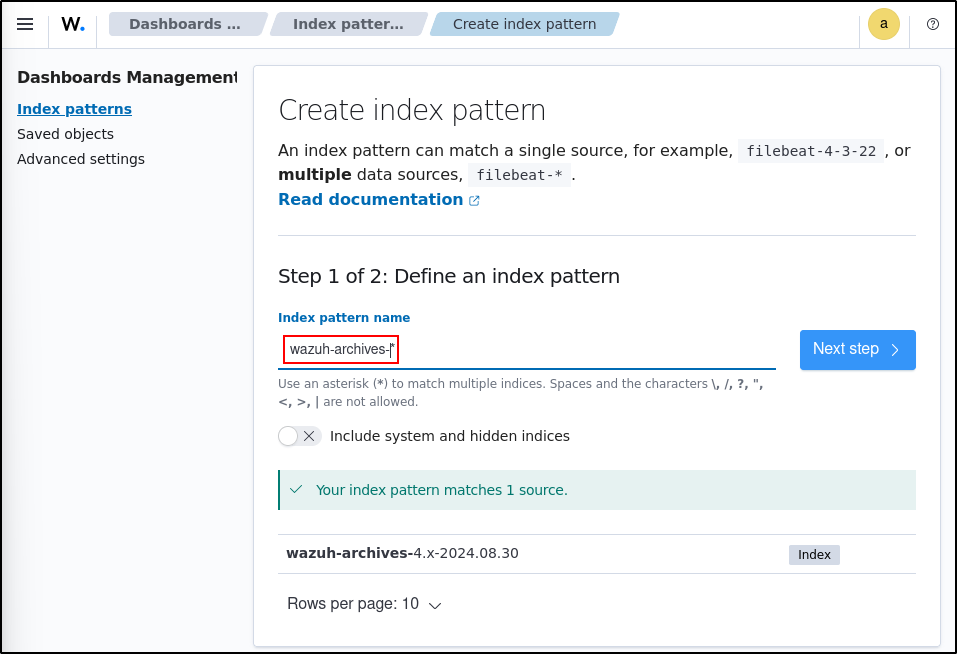
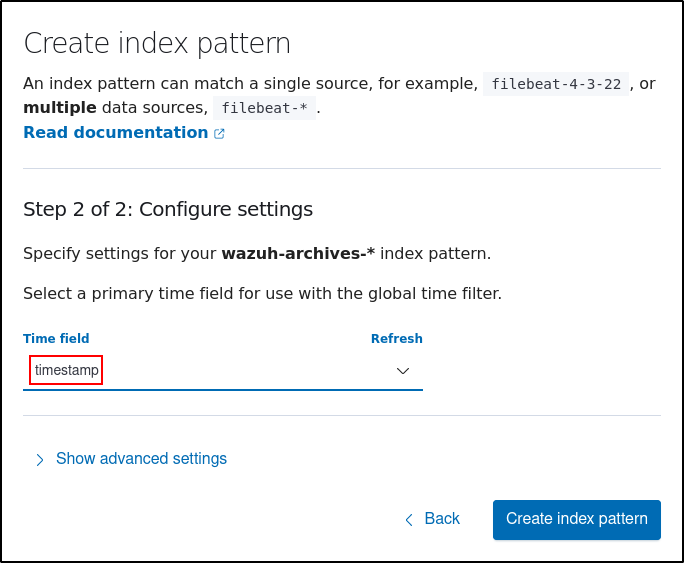
Click the upper-left menu icon and navigate to Dashboard management > Index patterns > Create index pattern. Use wazuh-archives-* as the index pattern name, and set timestamp in the Time field drop-down list.
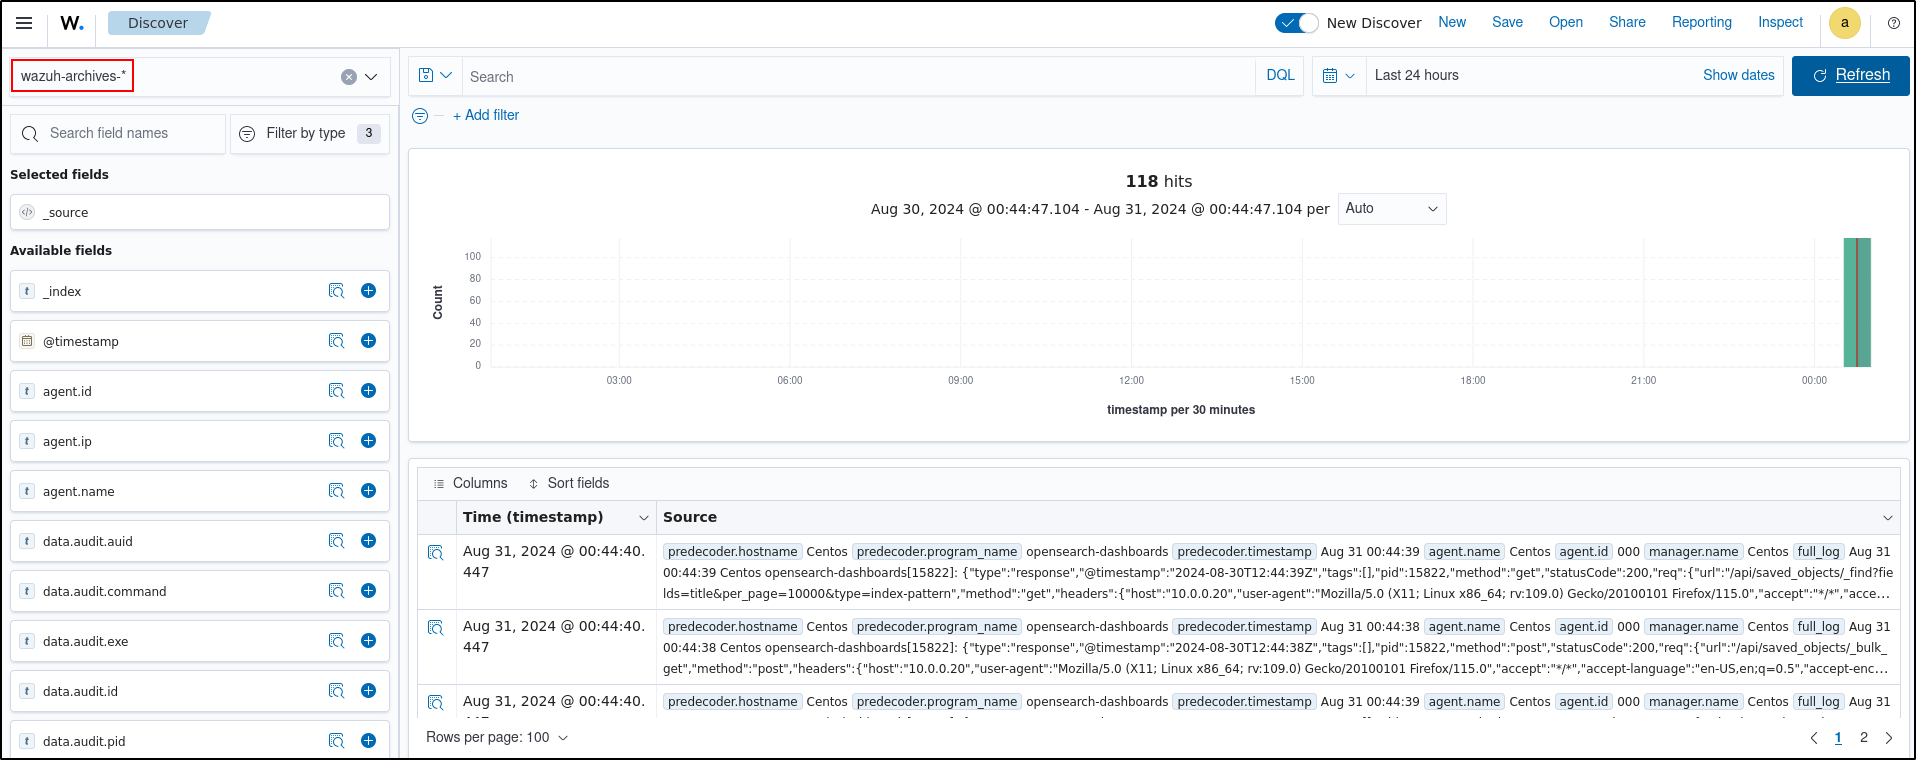
To view the events on the dashboard, click the upper-left menu icon and navigate to Discover. Change the index pattern to wazuh-archives-*.
Checkpoint: find an event that did not alert
Search wazuh-archives-* for a recent source event, confirm its timestamp and source identity, and determine whether a corresponding alert exists. Then check filesystem and index growth to establish an initial storage baseline.
Document the rollback: set archives.enabled back to false, restore the prior
logall and logall_json values, restart only the affected services, and verify
that new archive documents stop arriving. Treat deletion of existing indices as
a separate, explicitly approved retention action.